For example, I would like to check whether my user has enough authorization defined by authorization object s_carrid with value actvt = 03.
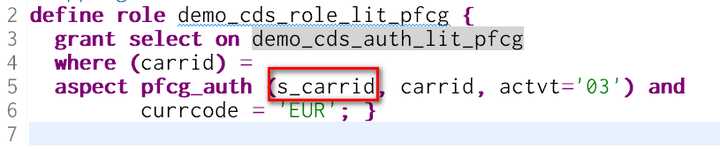
In tcode SU01, I can only see PFCG roles assigned to my user. Note that authorization object is not directly assigned to user but to PFCG roles. So, PFCG roles act as an intermediate layer:
User <- PFCG role <- Authorization Object
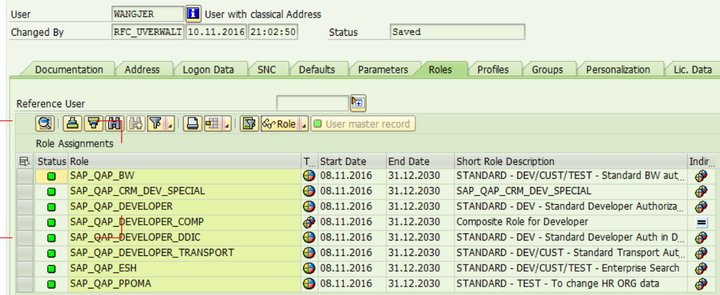
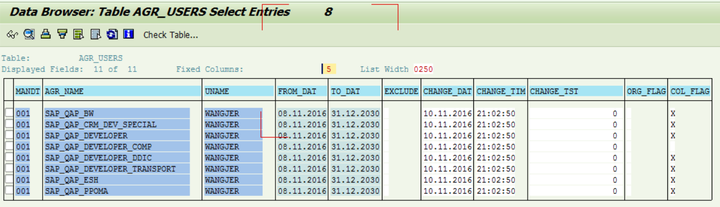
This table stores for a given user, what PFCG roles are assigned to it.
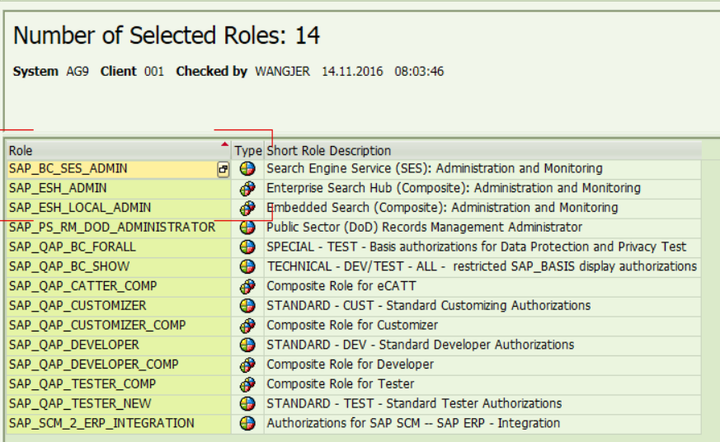
Now I need to figure out, which PFCG role has been assigned with authorization object S_CARRID?
Tcode SUIM:

The following PFCF roles have authorization object S_CARRID assigned:
Double click one of them, for example SAP_QAP_DEVELOPER:
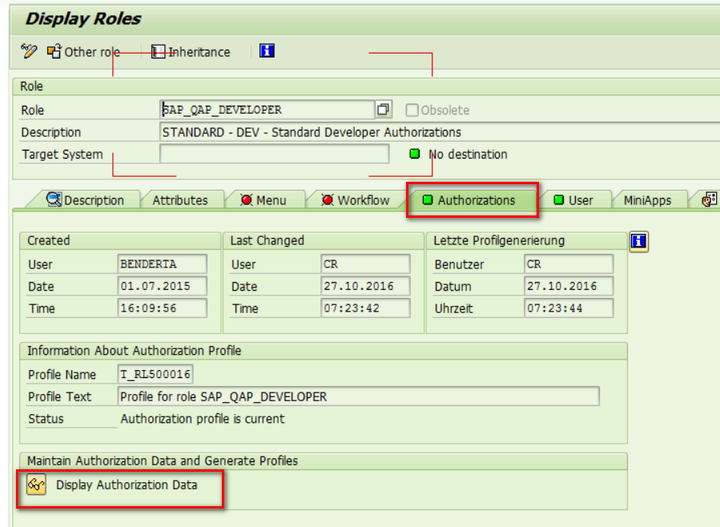
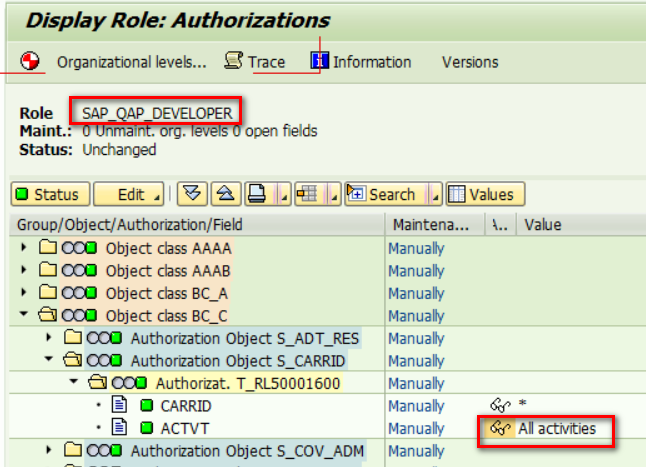
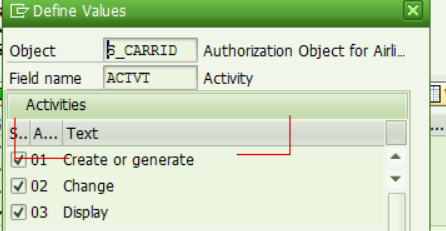
The above pictures mean: If a given user is assigned with PFCG role SAP_QAP_DEVELOPER, the user wil automatically have enough authorizations ( ACTVT 01, 02 and 03 all allowed ) defined by authorization object S_CARRID.
来自 “ ITPUB博客 ” ,链接:https://blog.itpub.net/24475491/viewspace-2674853/ ,如需转载,请注明出处,否则将追究法律责任。

