The OAuth 2.0 based authentication between SCP and C4C requires the same user-id to exist in both SAP Cloud Platform and SAP Hybris Cloud for Customer.
基于OAuth 2.0的SAP Cloud Platform和C4C single sign on的场景要能够工作,需要这两个系统里的user ID相同。
选择subaccount登录进去,选择Security菜单项下面的Trust,将Configuration Type设置为Custom,

将local provider name抄下来: https:// eu1.hana.ondemand.com/k f4i12wqm8
把Signing certificate字符串的值拷贝到一个文件里,另存为.cer文件:

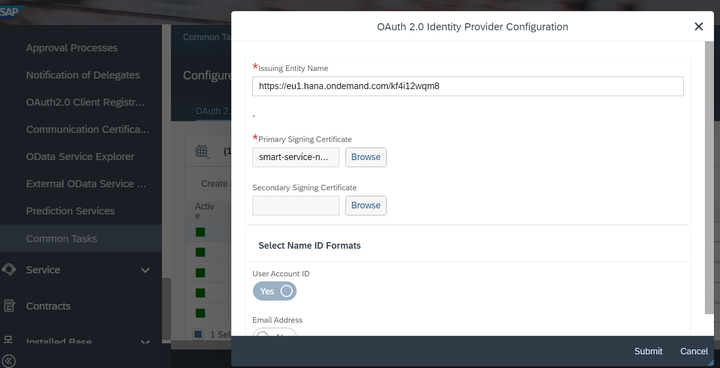
登录C4C系统QXL 233,Administrator工作中心,common task视图,Configure OAuth 2.0 Identity Provider:

新建一个OAuth 2.0 provider:

同样在Administrator的OAuth2.0 Client Registration里,新建一个OAuth 2.0 client:

Issuer Name字段的值,从下拉列表里选择刚刚新建的OAuth 2.0 Provider:
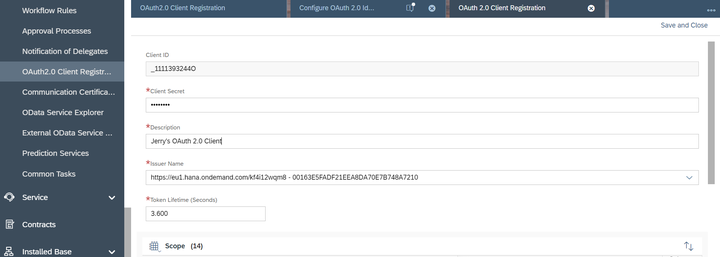
Scope字段,选择为CC_HOME:

新建成功:

进入Common task的Configure Single Sign-on:

把这个local service provider的值记录下来: qxl-cust233.dev.sapbydesign.com

在SAP Cloud Platform里,存在和ABAP Netweaver里SM59事务码创建的Destination类似的概念:
In SAP Cloud Platform, destinations are the ports that allow access to external systems based on various options. Extension apps then refer to these destinations to connect to their desired external systems.
部署在SAP Cloud Platform上的应用,通过这些Destination同外界连接。
在SAP Cloud Platform控制台的Connectivity里,创建一个新的destination:

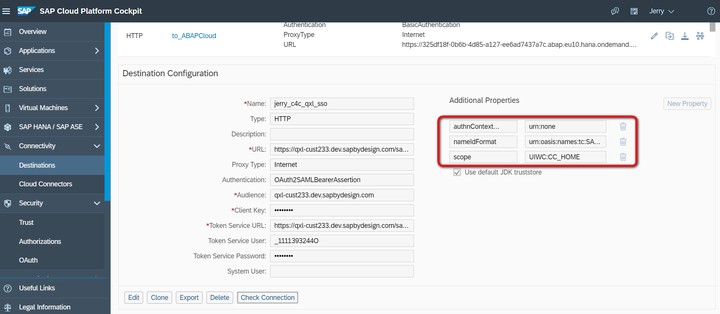
参考一个例子:

更多例子,参考博客: Configuring OAuth 2.0 between SAP Hybris Cloud for Customer and SAP Cloud Platform
来自 “ ITPUB博客 ” ,链接:https://blog.itpub.net/24475491/viewspace-2673903/ ,如需转载,请注明出处,否则将追究法律责任。

