微软官方发布了2022年02月的安全更新。本月更新公布了70个漏洞,包含17个特权提升漏洞、16个远程执行代码漏洞、6个信息泄露漏洞、5个拒绝服务漏洞、3个身份假冒漏洞、3个安全功能绕过漏洞以及1个篡改漏洞,其中50个漏洞级别为“Important”(严重)。 建议用户及时使用火绒安全软件(个人/企业)【漏洞修复】功能更新补丁。
涉及组件
· Azure Data Explorer
· Kestrel Web Server
· Microsoft Dynamics
· Microsoft Dynamics GP
· Microsoft Edge (Chromium-based)
· Microsoft Office
· Microsoft Office Excel
· Microsoft Office Outlook
· Microsoft Office SharePoint
· Microsoft Office Visio
· Microsoft OneDrive
· Microsoft Teams
· Microsoft Windows Codecs Library
· Power BI
· Roaming Security Rights Management Services
· Role: DNS Server
· Role: Windows Hyper-V
· SQL Server
· Visual Studio Code
· Windows Common Log File System Driver
· Windows DWM Core Library
· Windows Kernel
· Windows Kernel-Mode Drivers
· Windows Named Pipe File System
· Windows Print Spooler Components
· Windows Remote Access Connection Manager
· Windows Remote Procedure Call Runtime
· Windows User Account Profile
· Windows Win32K
以下漏洞需特别注意
Windows内核特权提升漏洞
CVE-2022-21989
严重级别:严重 CVSS:7.8
被利用级别:有可能被利用
成功利用该漏洞的攻击者可以进行特权提升后并执行恶意程序或访问资源。该漏洞已 被公开披露,暂未发现在野利用。
Microsoft Office Graphics 远程代码执行漏洞/Microsoft Office ClickToRun远程代码执行漏洞
CVE-2022-22003/CVE-2022-22004
严重级别:严重 CVSS:7.8
被利用级别:有可能被利用
用户交互触发该漏洞后,攻击者可利用该漏洞对受害者的计算机进行本地攻击。预览窗格不是该漏洞攻击媒介,因此不会触发漏洞。
Windows DNS Server远程代码执行漏洞
CVE-2022-21984
严重级别:严重 CVSS:8.8
被利用级别:有可能被利用
该漏洞在D NS 配置开启动态更新时容易被攻击者利用。成功利用该漏洞的攻击者可以在受害者电脑上执行任意代码。
修复建议
1 、通过火绒个人版 / 企业版【漏洞修复】功能修复漏洞。
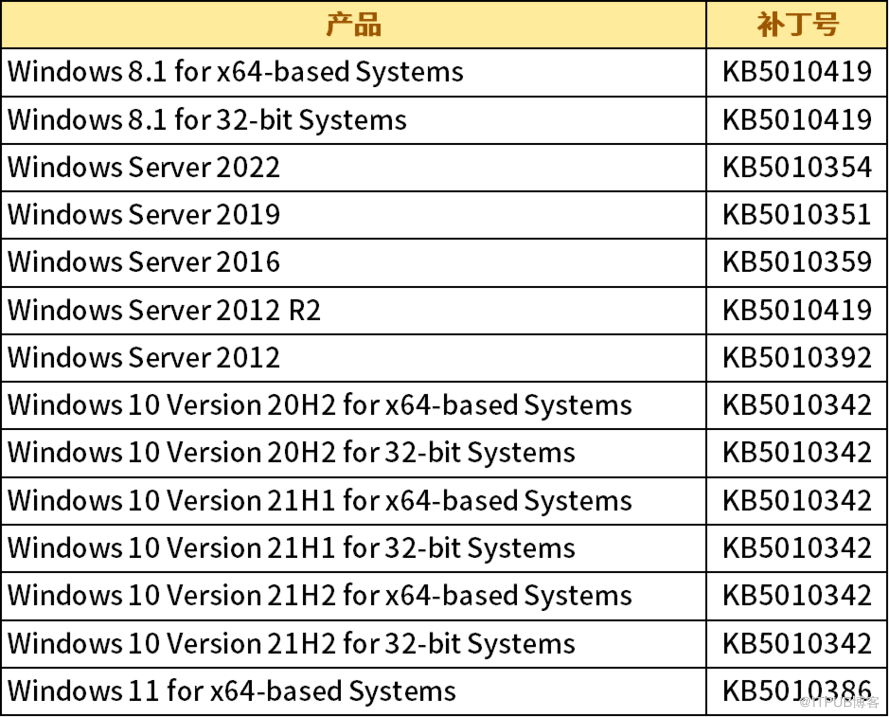
2 、下载微软官方提供的补丁
来自 “ ITPUB博客 ” ,链接:https://blog.itpub.net/70012241/viewspace-2855170/ ,如需转载,请注明出处,否则将追究法律责任。

