Pfx文件与单向SSL配置
pfx是什么文件
公钥加密技术12号标准(Public Key Cryptography Standards #12,PKCS#12)为存储和传输用户或服务器私钥、公钥和证书指定了一个可移植的格式。它是一种二进制格式,这些文件也称为PFX文件。开发人员通常需要将PFX文件转换为某些不同的格式,如PEM或JKS,以便可以为使用SSL通信的独立Java客户端或WebLogic Server使用。是一种Microsoft协议,使得用户可以将机密信息从一个环境或平台传输到另一个环境或平台。使用该协议,用户就可以安全地将个人信息从一个计算机系统导出到另一个系统中。
单向SSL配置
生成 SSL证书命令:
sudo keytool -genkey -keyalg RSA -dname “cn=localhost,ou=none,o=none,l=shanghai,st=shanghai,c=cn” -alias server -keypass 123456 -keystore server.keystore -storepass 123456 -validity 3650
生成CSR文件
sudo keytool -certReq -alias server -keystore server.keystore -file ca.csr -storepass 123456
生成CER文件
- 因为我们生成的证书使用keytool生成的,没有经过操作系统可信任的CA机构颁发,所以当用浏览器访问时,会出现不信任证书警告,我们手工将cer文件(服务端公钥)导入浏览器的证书列表,让其信任。
sudo keytool -export -alias server -keystore server.keystore -file ca.cer -storepass 123456
在Tomcat中配置Https证书
在serve.xml 中添加如下配置,即可访问https的站点了。
<Connector SSLEnabled=”true” clientAuth=”false”
keystoreFile=”/Users/beiyan/Documents/test/server.keystore”
keystorePass=”123456″ maxThreads=”150″ port=”8443″
protocol=”org.apache.coyote.http11.Http11NioProtocol” scheme=”https”
secure=”true” sslProtocol=”TLS” />
其中keystoreFile 为证书的地址,keystorePass 为证书的密码。
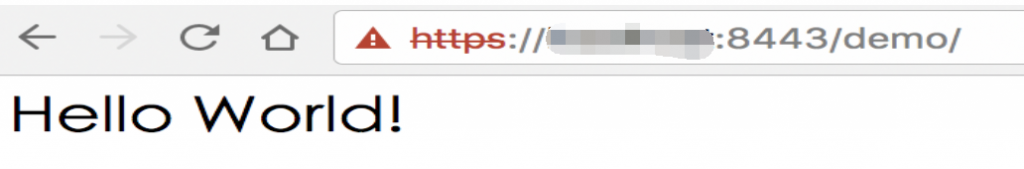
访问界面如下:
导入CER文件,让浏览器信任此证书
- 双击cer 即可导入,再设置为 始终信任 ,再次访问

应用程序访问
- 如果使用HttpClient 等工具访问该Https连接时,需要讲ca.cer 导入jre中;
命令如下:keytool -import -alias tomcatsso -file “ca.cer” -keystore “/Library/Java/JavaVirtualMachines/jdk1.8.0_111.jdk/Contents/Home/jre/lib/security/cacerts” -storepass 123456
其中/Library/Java/JavaVirtualMachines/jdk1.8.0_111.jdk/Contents/Home/jre 是jre目录 123456 是jre默认的密码
来自 “ ITPUB博客 ” ,链接:https://blog.itpub.net/31483669/viewspace-2678421/ ,如需转载,请注明出处,否则将追究法律责任。

